Before the rebuild, michaelpierce.com exposed its backup files, sent no security headers, and kept its private galleries behind obscure URLs, and one day later it was a hardened portfolio. A small business site in that condition is the quickest kind of AI-accelerated project we take on.
A Legacy Site with Hidden Risks
The legacy codebase had zero HTTP security headers: no Content-Security-Policy, no HSTS, no X-Frame-Options. Directory listing was enabled, exposing the full file structure to anyone who knew where to look. Sensitive backup files (.old, .bak, .sql) were publicly accessible. Private photo content was protected by nothing more than obscure URLs, with no authentication, session management, or access control.
PHP scripts lacked input validation and output encoding, opening the door to injection attacks. There was no CSRF protection on forms, no rate limiting on login attempts, and server information was freely disclosed in response headers. The site had no sitemap, structured metadata, or SEO optimization. A refresh would not have touched any of it, so the site needed a complete rebuild from the ground up.

Vibe-Coding: Complete Rebuild in a Single Day
A senior architect directed Claude AI through a phased rebuild rather than a patch job. The work started with a clean dark sci-fi landing page and animated hero, then moved to a security audit that stripped every insecure script. Next came a gallery system with public and private tiers, authentication with bcrypt and rate limiting, and SEO-friendly URLs, followed by a hardening pass that locked down the Apache configuration, with 8 HTTP security headers in place by the last commit.
Twelve commits, each one a distinct phase of work, ran from the initial landing page through the final SEO improvements, with a human who understands production-grade security architecting every line before Claude executed it. Every file on the site had been replaced and every vulnerability eliminated by the end.

✕ Issues Found
- ✕Plain-text database passwords in PHP files
- ✕Unrestricted shell command execution
- ✕phpinfo() exposed with no authentication
- ✕Google Analytics tracking with no privacy policy
- ✕Table-based layout, Comic Sans typography
- ✕No responsive design (broken on mobile)
- ✕No HTTPS enforcement
- ✕No SEO metadata, sitemap, or structured data
- ✕Scattered legacy files across 20+ directories
- ✕No security headers (CSP, HSTS, X-Frame)
✓ Improvements
- ✓Dark sci-fi theme with animated RV landing
- ✓All insecure scripts and credentials removed
- ✓7 public photo galleries with lightbox viewer
- ✓Password-protected private family gallery
- ✓Full SEO: sitemap, llms.txt, canonical URLs
- ✓Security headers (CSP, HSTS, X-Frame-Options)
- ✓Responsive design for mobile, tablet, and desktop
- ✓PHP login rate limiting (brute-force protection)
- ✓3 legacy articles converted to modern HTML
- ✓Clean codebase with zero exposed credentials
A Secure, Modern Portfolio
Photo Gallery System
7 public galleries with cover photos, masonry grid layout, vanilla JavaScript lightbox, keyboard navigation, and dynamic photo counts
Private Galleries
Bcrypt-authenticated private galleries for personal and family content with separate login flows, file-based sessions, and rate-limited access
Security Hardening
8 HTTP security headers including CSP, HSTS, and X-Frame-Options. Blocked sensitive file types, disabled directory listing, and locked down Apache
SEO Foundation
Canonical URLs, XML sitemap, robots.txt, llms.txt for AI crawlers, structured metadata, and SEO-friendly gallery slugs via mod_rewrite
Dark Sci-Fi Design
Animated star field hero, typing effect subtitle, RV animation strip, glowing dividers, and a fully responsive dark theme, totaling 1,970 lines of hand-crafted CSS
Authenticated Image Serving
PHP image proxy that serves private gallery photos exclusively through validated sessions, so there is no direct URL access, hotlinking, or way around the session check
See It in Action
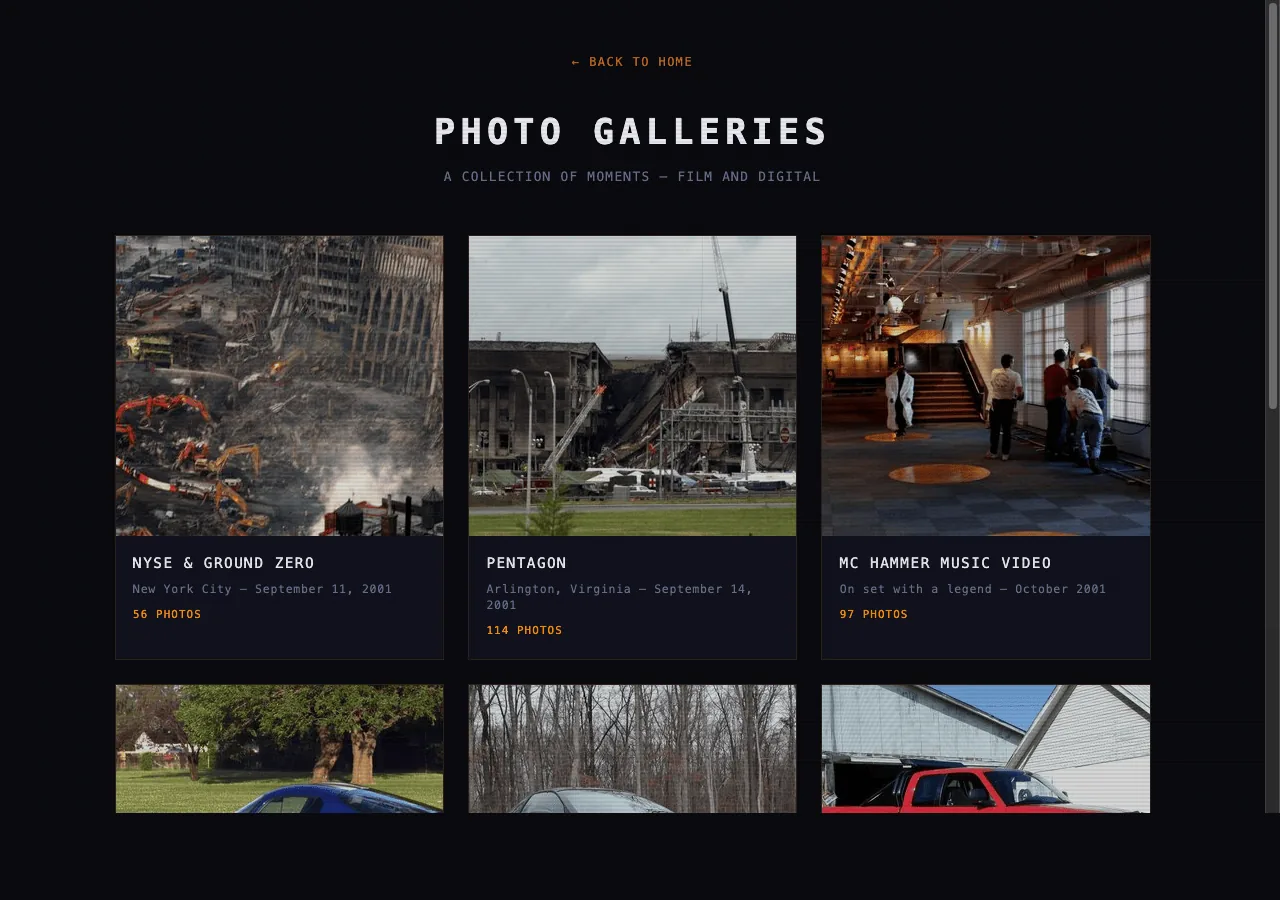
Photo Galleries
Seven public galleries spanning historical photography, automotive collections, and behind-the-scenes moments. Each gallery card shows a cover photo, title, description, and dynamic photo count pulled from the server at render time. The gallery index is built with PHP and styled with a responsive grid that adapts from a 3-column desktop layout to a single-column mobile view.

Gallery Viewer
Each gallery opens with its original story text, the context
behind the photos, written by the photographer. Below, a
masonry-style thumbnail grid displays every photo in the
collection. Clicking any thumbnail opens a full-screen
lightbox built in vanilla JavaScript with keyboard
navigation, swipe support, and smooth transitions.
SEO-friendly URLs like
/gallery/nyc/
are powered by Apache mod_rewrite rules.

Personal Landing Page
The homepage opens with an animated star field and a bold title rendered in a custom monospace font with glowing brackets. A typing effect cycles through roles (Father, Tech Entrepreneur, Photographer, World Traveler) while an SVG RV animation drives across the bottom of the viewport. Below the fold are the bio section and a preview of the gallery grid. The entire landing experience is built with vanilla JavaScript, no external dependencies.
Security Hardening
| Area | Before | After |
|---|---|---|
| HTTP Security Headers | 0 headers | 8 headers (CSP, HSTS, X-Frame-Options, X-Content-Type-Options, XSS-Protection, Referrer-Policy, Permissions-Policy, X-Permitted-Cross-Domain-Policies) |
| Authentication | None | Bcrypt hashes + file-based sessions |
| Login Protection | None | Rate limiting: 5 attempts per 5 minutes per IP |
| Directory Listing | Enabled | Disabled (Options -Indexes) |
| Sensitive Files | Publicly accessible | Blocked (.old, .bak, .sql, .cfg, .ini, .log) |
| Private Content | URL-guessable | Session-authenticated image proxy |
| Output Encoding | None | htmlspecialchars() on all output |
| CSRF Protection | None | Token-based form validation |
Technology Stack
Frontend
Backend & Security
Zero Dependencies, Zero Frameworks
Every line of JavaScript on michaelpierce.com is vanilla, with no jQuery, React, or build tools. The star field animation, typing effect, lightbox viewer, and keyboard navigation are all hand-written. The CSS is 1,970 lines of custom styles with no framework underneath. The PHP backend uses no Composer packages, ORM, or routing library, which is why the site has zero supply-chain risk. The result is a site that loads instantly and can be understood by reading the source files directly.
The Vibe-Coding Advantage
The site gained a new design, a new codebase, security hardening, a gallery system with 400+ photos, and an SEO foundation in a single day, with the same security review a multi-week engagement would have produced.
Complete Rewrite
The whole site was rebuilt, with security as a first-class requirement from the first file.
Security-First
8 HTTP security headers, authenticated image serving, rate-limited login, CSRF tokens, and blocked file types, all built in from day one.
One Day, One Team
A senior architect working with AI means no coordination overhead and no handoffs, and twelve commits took the site from first line to final deployment in a single working session.
What This Would Cost the Traditional Way
Rebuilding a personal portfolio site with this level of security hardening, gallery functionality, and custom design would typically take a freelance developer or small agency 2–4 weeks. The security audit, custom PHP development, gallery system, authentication flows, SEO setup, and design work would fall to separate specialists or a full-stack developer billing for significant hours.
At market rates for security-conscious PHP development, the range is $5,000 to $15,000, before counting the back-and-forth on design iterations and scope changes or the delays that come with traditional project timelines.
More Simple Site Redesigns

Tell Us What You Want Built
We rebuilt and hardened a site with a dozen live vulnerabilities in a single day, and we will scope the cost and timeline once you tell us what you need.